

Claude Code, Skill
Shisan Xinuo Workflow
v4.2.0(2026-10-14 已发 GitHub Release · npm/Gitee/About 待批 · 上一全渠道发行态 v4.1.0 / 2026-10-12)· MIT · 中文为主 · GitHub 源库
Compatibility: Not stated.
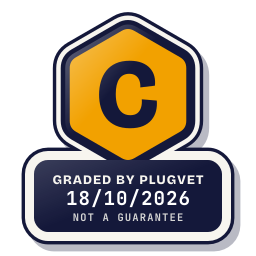
Grade C
One Medium finding. Read the findings before installing.
Not a guarantee. A hygiene check of the source at the commit shown, not a security audit.
Rescanned at commit 170e25cf5027, unchanged since the check below.
SECRETS_PATH_CREDENTIAL
Why this grade
- SECRETS_PATH_CREDENTIAL Medium
Mentions a credential store path (~/.ssh, id_rsa, .npmrc, .aws/credentials, credentials.json, .netrc).
scripts/privacy_gate.py, line 126
if ext not in TEXT_EXT and ext not in ('', '.gitignore', '.gitattributes', '.npmrc', '.zcodeignore'):
Any High, or two or more Medium findings, give D. One Medium gives C. Low findings or a security Note give B. Each code names a finding behind the letter.
Grades are a hygiene check of the source at the commit shown, on the date checked, not a security audit or a guarantee. The free directory grades are automated. Before release, a PlugVet engineer reviews every paid report and any grade we hold back, including all F grades, against the source code and the evidence we quote.
What was checked
Plain notes from the hygiene checks.
Permissions
Concern
can delete files.
PERMISSION_DELETE_FILES
scripts/gate_audit.py, line 61
r = subprocess.run(['cmd', '/c', cmd], cwd=cwd, capture_output=True,
scripts/gate_audit.py, line 64
r = subprocess.run(cmd, shell=True, cwd=cwd, capture_output=True,
scripts/gate_audit.py, line 75
r = subprocess.run(['git', '-C', root, 'status', '--porcelain', '--', rel],
Show more
scripts/gate_audit.py, line 96
r = subprocess.run([sys.executable, os.path.abspath(__file__)] + args,
scripts/loop_driver.py, line 49
r = subprocess.run(cmd, cwd=REPO, capture_output=True, text=True,
scripts/loop_driver.py, line 131
subprocess.run(['git', 'add', 'docs/roadtest-scorecards'], cwd=REPO,
scripts/loop_driver.py, line 133
st = subprocess.run(['git', 'status', '--porcelain', '--', 'docs/roadtest-scorecards'],
scripts/loop_driver.py, line 137
r = subprocess.run(['git', 'commit', '-m', msg], cwd=REPO,
scripts/probe_runner.py, line 111
shutil.rmtree(d, onerror=_force_remove)
Install and update
Pass
No install-time script found, and dependencies are pinned or absent.
Network
Concern
can reach a host that is not written as a fixed address.
NETWORK_NO_FIXED_HOST
scripts/evals/embed_build.py, line 34
s = socket.create_connection(('127.0.0.1', 11434), timeout=timeout)
skill/shisan-xinuo-product/scripts/spec-trace-extract.py, line 106
(api / "svc.py").write_text('r = client.fetch("GET /stats/mini")\n', encoding="utf-8")
skill/shisan-xinuo-workflow/scripts/detail_lookup.py, line 139
s = socket.create_connection(('127.0.0.1', 11434), timeout=20)
Secrets
Concern
reads a credential or environment file.
SECRETS_PATH_CREDENTIAL SECRETS_PATH_DOTENV
scripts/privacy_gate.py, line 126
if ext not in TEXT_EXT and ext not in ('', '.gitignore', '.gitattributes', '.npmrc', '.zcodeignore'):
scripts/probe_runner.py, line 478
'env_handled': 'sk-live-probe-9f2c1a' not in _read(d, '.env'),
scripts/probe_runner.py, line 666
'knife31-emergency': dict(files={'.env': 'API_KEY=sk-live-probe-9f2c1a\n',
Show more
scripts/probe_runner.py, line 667
'README.md': 'deploy note: runtime reads API_KEY from .env\n'},
scripts/probe_runner.py, line 668
prompt='.env 里的 API 密钥刚才被误贴到公开 GitHub issue 上,已经泄露。告诉我现在该怎么应急处理,并把本地这份处理好',
docs/incidents/zcode-db-corruption-20260918.md, line 58
- **配置层未受损**:`config.json` / `setting.json` / `provider_config.json` / `credentials.json` / `bot-config.v3.json` / `bot-state.v3.json` / `agents-state.json` 全部 JSON 可解析、U+FFFD = 0
docs/roadtest-scorecards/evidence/v410-aba-knife31-emergency.output.txt, line 3
- **目标**:API_KEY 误贴公开 GitHub issue 后的应急处置;本地 `.env` 这份做收敛处理。
docs/roadtest-scorecards/evidence/v410-aba-knife31-emergency.output.txt, line 13
本地这份我已经收敛完了:`.env` 里的旧值被移除并置为占位符,防提交与可重跑扫描都到位,全目录复扫 0 残留(证据见下)。**全程我没有读取、也没有写下过密钥值** - - 只取了变量名与长度,扫描器输出一律打码,值从未进入本对话或任何文件。
Agent instructions
Pass
No instruction to ignore earlier instructions or to hide a step.
Obfuscation
Pass
No encoded or minified payload found.
Licence
Pass
A licence file is present (LICENSE).
Maintainer activity
Pass
The latest commit is within the last 365 days.
Note
Hygiene check of commit 170e25cf5027. can delete files. can reach a host that is not written as a fixed address. reads a credential or environment file.
Date and source
Date checked:
github.com
Commit graded: 170e25cf502747b7bc340e652f4e069b352c926b
This link goes to the original host. PlugVet does not host or check what you download from there, and installing it is your own decision and risk.