

Codex, Plugin
Codex 13 Plugin Suite
不是让小白变成程序员,而是让小白能把项目流程说清楚。
Compatibility: Not stated.
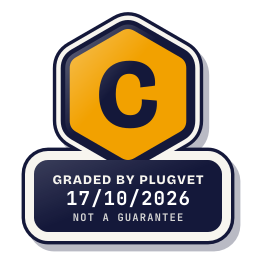
Grade C
One Medium finding. Read the findings before installing.
Not a guarantee. A hygiene check of the source at the commit shown, not a security audit.
Rescanned at commit 199eb851342f, unchanged since the check below.
PERMISSION_SHELL_UNDECLARED
Why this grade
- PERMISSION_SHELL_UNDECLARED Medium
Runs shell commands that the manifest or description does not mention.
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 801
revs = subprocess.run(["git", "-C", str(project), "rev-list", "--all", f"--max-count={max_commits}"], text=True, stdout=subprocess.PIPE, stderr=subprocess.DEVNULL, timeout=10)
Any High, or two or more Medium findings, give D. One Medium gives C. Low findings or a security Note give B. Each code names a finding behind the letter.
Grades are a hygiene check of the source at the commit shown, on the date checked, not a security audit or a guarantee. The free directory grades are automated. Before release, a PlugVet engineer reviews every paid report and any grade we hold back, including all F grades, against the source code and the evidence we quote.
What was checked
Plain notes from the hygiene checks.
Permissions
Concern
requests shell access. No manifest field names shell or command execution.
PERMISSION_SHELL_UNDECLARED
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 801
revs = subprocess.run(["git", "-C", str(project), "rev-list", "--all", f"--max-count={max_commits}"], text=True, stdout=subprocess.PIPE, stderr=subprocess.DEVNULL, timeout=10)
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 811
grep = subprocess.run(["git", "-C", str(project), "grep", "-I
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1903
completed = subprocess.run([name, "--version"], stdout=subprocess.DEVNULL, stderr=subprocess.DEVNULL)
Show more
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/validate_skill.py, line 109
completed = subprocess.run(cmd, cwd=str(cwd), text=True, stdout=subprocess.PIPE, stderr=subprocess.STDOUT)
Install and update
Pass
No install-time script found, and dependencies are pinned or absent.
Network
Concern
can reach a host that is not written as a fixed address.
NETWORK_NO_FIXED_HOST
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1257
if "fetch(" in r.text.lower() and "request.url" in r.text.lower():
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1512
with urllib.request.urlopen(req, timeout=5) as resp:
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1767
const res = await fetch(BASE_URL.replace(/\\/$/, "") + route.path, {{ method, headers, body }});
Show more
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1859
("Third-party API", text_feature(ctx, ["fetch(", "axios", "requests.", "httpclient"])),
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_gate.py, line 570
if has_any(lower, ["tool_calls", "function_call", "execute", "exec(", "child_process", "shell", "sendemail", "sendsms", "delete", "writefile", "readfile", "fetch("]):
Secrets
Concern
reads a credential or environment file.
SECRETS_ENV_READ SECRETS_PATH_DOTENV
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 112
".json", ".yaml", ".yml", ".toml", ".ini", ".env", ".example",
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 564
if r.rel.lower().endswith(".env") and not r.rel.lower().endswith(".env.example") and re.search(r"(?i)(secret|token|password|api[_-]?key)\s*=\s*[^#\n]{8,}", r.text):
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 565
add(findings, seen, title=".env file with secret-like values is present", severity="critical", category="Secrets", file=r.rel, line=1, evidence=r.rel,
Show more
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 566
impact=".env files often contain production secrets.",
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 567
recommendation="Remove the real .env from the repository and rotate exposed values.",
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 568
minimum_fix="Delete .env and add it to .gitignore.",
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 569
standard_fix="Use .env.example placeholders and deployment secret injection.",
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1493
i/sms", "/robots.txt", "/sitemap.xml", "/.env", "/static/js/main.js.map"]
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1758
const USER_AUTH = process.env.USER_TOKEN || "";
codex-project-plugin-suite/plugins/security-release-review/skills/security-release-review/scripts/security_audit.py, line 1759
const ADMIN_AUTH = process.env.ADMIN_TOKEN || "";
Agent instructions
Pass
No instruction to ignore earlier instructions or to hide a step.
Obfuscation
Pass
No encoded or minified payload found.
Licence
Pass
A licence file is present (LICENSE).
Maintainer activity
Pass
The latest commit is within the last 365 days.
Note
Hygiene check of commit 199eb851342f. requests shell access. No manifest field names shell or command execution. can reach a host that is not written as a fixed address. reads a credential or environment file.
Date and source
Date checked:
github.com
Commit graded: 199eb851342fabcd2e1aed123a5f3195439f9bbf
This link goes to the original host. PlugVet does not host or check what you download from there, and installing it is your own decision and risk.