

MCP, MCP server
Mcp Slim Guard
MCP Slim Guard gives a host one deliberate way to reach authorized upstream tools.
Compatibility: Not stated.
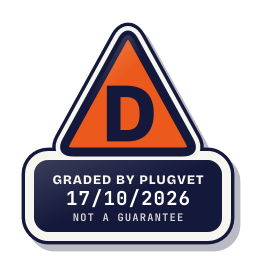
Grade D
Two or more Medium findings, or a High finding. Only try it in a sandbox.
Not a guarantee. A hygiene check of the source at the commit shown, not a security audit.
Rescanned at commit a5596a0131c2, unchanged since the check below.
INSTALL_LIFECYCLE_HOOK SECRETS_PATH_CREDENTIAL
Why this grade
- INSTALL_LIFECYCLE_HOOK Medium
A package install hook (preinstall, install, postinstall or prepare) runs a script.
package.json, line 85
prepare - SECRETS_PATH_CREDENTIAL Medium
Mentions a credential store path (~/.ssh, id_rsa, .npmrc, .aws/credentials, credentials.json, .netrc).
scripts/integration/package-native-real-server-smoke.mjs, line 212
const emptyNpmConfig = path.join(temporaryRoot, ".npmrc");
Any High, or two or more Medium findings, give D. One Medium gives C. Low findings or a security Note give B. Each code names a finding behind the letter.
Grades are a hygiene check of the source at the commit shown, on the date checked, not a security audit or a guarantee. The free directory grades are automated. Before release, a PlugVet engineer reviews every paid report and any grade we hold back, including all F grades, against the source code and the evidence we quote.
What was checked
Plain notes from the hygiene checks.
Permissions
Concern
can delete files.
PERMISSION_DELETE_FILES
scripts/benchmark.mjs, line 78
if (fs.existsSync(AUDIT_LOG)) fs.unlinkSync(AUDIT_LOG);
scripts/build.mjs, line 15
fs.rmSync(outputDirectory, { recursive: true, force: true });
scripts/smoke-test.mjs, line 41
fs.rmSync(TEST_DIR, { recursive: true, force: true });
Show more
scripts/smoke-test.mjs, line 75
const proc = child_process.spawn("node", [GUARD_CLI, "start", "--mode", "native"], {
scripts/candidate/create-source-snapshot.mjs, line 368
await fs.rm(temporaryDirectory, { recursive: true, force: true });
scripts/demo/alpha-demo.mjs, line 125
fs.rmSync(temporaryDirectory, { recursive: true, force: true });
scripts/evaluation/mode-protocol-replay.mjs, line 201
fs.rmSync(temporaryDirectory, { recursive: true, force: true });
scripts/integration/codex-config-smoke.mjs, line 51
fs.rmSync(temporaryDirectory, { recursive: true, force: true });
scripts/integration/package-native-real-server-smoke.mjs, line 451
fs.rmSync(temporaryRoot, {
Install and update
Concern
runs a script at install time.
INSTALL_LIFECYCLE_HOOK
package.json, line 85
prepare
Network
Pass
No network call found.
Secrets
Concern
reads a credential or environment file.
SECRETS_ENV_READ SECRETS_PATH_CREDENTIAL SECRETS_PATH_DOTENV
scripts/benchmark/fixtures.mjs, line 194
if (source.name === "github" && !process.env.GITHUB_TOKEN) {
scripts/candidate/create-source-snapshot.mjs, line 62
const SENSITIVE_FILENAME_MARKERS = Object.freeze([".env", "auth", "cookie", "credential", "secret", "token"]);
scripts/integration/package-native-real-server-smoke.mjs, line 212
const emptyNpmConfig = path.join(temporaryRoot, ".npmrc");
Show more
scripts/candidate/create-source-snapshot.mjs, line 89
return lower === ".env" || lower.startsWith(".env.") || SENSITIVE_FILENAME_PATTERN.test(lower);
scripts/integration/real-server-smoke.mjs, line 47
if (process.env.GITHUB_PERSONAL_ACCESS_TOKEN) {
scripts/integration/real-server-smoke.mjs, line 48
return { value: process.env.GITHUB_PERSONAL_ACCESS_TOKEN, source: "environment" };
scripts/benchmark/fixtures.mjs, line 164
env: { ...process.env, ...env },
Agent instructions
Pass
No instruction to ignore earlier instructions or to hide a step.
Obfuscation
Concern
contains an encoded blob in a file that should be readable.
OBFUSCATION_ENCODED_BLOB
docs/evidence/2026-08-06-mode-result-projection.json, line 921
"preview": "{\"content\":[{\"type\":\"text\",\"text\":\"metadata fixture\"}],\"_meta\":{\"trace\":\"xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx
docs/evidence/2026-08-06-mode-result-projection.json, line 1870
"preview": "{\"content\":[{\"type\":\"text\",\"text\":\"metadata fixture\"}],\"_meta\":{\"trace\":\"xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx
Licence
Pass
A licence file is present (LICENSE).
Maintainer activity
Pass
The latest commit is within the last 365 days.
Note
Hygiene check of commit a5596a0131c2. can delete files. runs a script at install time. reads a credential or environment file. contains an encoded blob in a file that should be readable.
Date and source
Date checked:
github.com
Commit graded: a5596a0131c2e6adad497e1bc381c04e7d1a3bc5
This link goes to the original host. PlugVet does not host or check what you download from there, and installing it is your own decision and risk.