

MCP, MCP server
SSH Session MCP
SSH Session MCP, an MCP server listed in the PlugVet directory.
Compatibility: Not stated.
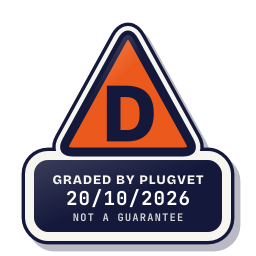
Grade D
Two or more Medium findings, or a High finding. Only try it in a sandbox.
Not a guarantee. A hygiene check of the source at the commit shown, not a security audit.
Rescanned at commit 01e5039eba5a, unchanged since the check below.
PERMISSION_SHELL_UNDECLARED INSTALL_LIFECYCLE_HOOK OBFUSCATION_ENCODED_BLOB
Why this grade
- PERMISSION_SHELL_UNDECLARED Medium
Runs shell commands that the manifest or description does not mention.
src/distributed.ts, line 213
return this.commands.get(commandIdValue); - INSTALL_LIFECYCLE_HOOK Medium
A package install hook (preinstall, install, postinstall or prepare) runs a script.
package.json, line 25
prepare - OBFUSCATION_ENCODED_BLOB Medium
Contains a long base64 shaped string in a file that should be readable.
src/viewer-html/page-shell.ts, line 22
="icon" href="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHZpZXdCb3g9IjAgMCAzMiAzMiI+PHJlY3Qgd2lkdGg9IjMyIiBoZWlnaHQ9IjMyIiByeD0iNiIgZmlsbD0iIzEx
Any High, or two or more Medium findings, give D. One Medium gives C. Low findings or a security Note give B. Each code names a finding behind the letter.
Grades are a hygiene check of the source at the commit shown, on the date checked, not a security audit or a guarantee. The free directory grades are automated. Before release, a PlugVet engineer reviews every paid report and any grade we hold back, including all F grades, against the source code and the evidence we quote.
What was checked
Plain notes from the hygiene checks.
Permissions
Concern
requests shell access. No manifest field names shell or command execution. can delete files.
PERMISSION_SHELL_UNDECLARED PERMISSION_DELETE_FILES
src/distributed.ts, line 213
return this.commands.get(commandIdValue);
src/server-state.ts, line 1417
await fs.unlink(RUNTIME_PATHS.serverInfoFile);
Install and update
Concern
runs a script at install time.
INSTALL_LIFECYCLE_HOOK
package.json, line 25
prepare
Network
Concern
can reach a host that is not written as a fixed address.
NETWORK_NO_FIXED_HOST
scripts/ctl.mjs, line 244
const response = await fetch(url);
scripts/install-trivy.sh, line 12
curl -fsSL "${TRIVY_BASE_URL}/${TRIVY_ARCHIVE}" -o "${TRIVY_ARCHIVE}"
scripts/install-trivy.sh, line 13
curl -fsSL "${TRIVY_BASE_URL}/${TRIVY_CHECKSUMS}" -o "${TRIVY_CHECKSUMS}"
Show more
src/viewer-cli.ts, line 198
const response = await fetch(url);
src/viewer-cli.ts, line 208
const response = await fetch(attachUrl(config, suffix), {
src/viewer-cli.ts, line 469
ws = new WebSocket(url);
src/viewer-html/home-page.ts, line 39
// fetch("/api/sessions")
src/viewer-html/home-page.ts, line 95
// fetch("/api/sessions")
Dockerfile, line 51
CMD ["node", "-e", "const port=(process.env.VIEWER_PORT||'8793').trim(); if (port==='0') process.exit(0); fetch(`http://127.0.0.1:${port}/readyz`).then((response)=>{ if(!response.o
docker-compose.env.yml, line 34
test: ["CMD", "node", "-e", "fetch('http://127.0.0.1:8793/readyz').then((response)=>{if(!response.ok)process.exit(1);}).catch(()=>process.exit(1));"]
docker-compose.yml, line 28
test: ["CMD", "node", "-e", "fetch('http://127.0.0.1:8793/readyz').then((response)=>{if(!response.ok)process.exit(1);}).catch(()=>process.exit(1));"]
Secrets
Concern
reads a credential or environment file.
SECRETS_ENV_READ SECRETS_PATH_DOTENV
scripts/build-site.mjs, line 501
['Runtime config', '运行时配置', 'Use `.env` for one target and `ssh-session-mcp.co
scripts/ctl.mjs, line 18
const ENV_PATH = resolve(ROOT, '.env');
scripts/ctl.mjs, line 89
join(WORKSPACE_ROOT, '.env'),
Show more
scripts/ctl.mjs, line 105
// ignore missing .env candidates
src/repo-validation.ts, line 12
'.env.example',
src/repo-validation.ts, line 86
const envExamplePath = join(rootDir, '.env.example');
src/repo-validation.ts, line 136
failures.push(`.env.example is missing required token: ${token}`);
src/server-state.ts, line 252
// ── .env loader & argv parser ────────────────────────────────────────────────
src/server-state.ts, line 344
export const DEFAULT_KEY = argvConfig.key || process.env.SSH_KEY;
src/server-state.ts, line 345
export const DEFAULT_KEY_FILE_CONTENT = argvConfig.key ? undefined : readOptionalSecretFile(process.env.SSH_KEY_FILE, 'SSH_KEY_FILE');
Agent instructions
Pass
No instruction to ignore earlier instructions or to hide a step.
Obfuscation
Concern
contains an encoded blob in a file that should be readable.
OBFUSCATION_ENCODED_BLOB
src/viewer-html/page-shell.ts, line 22
="icon" href="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHZpZXdCb3g9IjAgMCAzMiAzMiI+PHJlY3Qgd2lkdGg9IjMyIiBoZWlnaHQ9IjMyIiByeD0iNiIgZmlsbD0iIzEx
Licence
Pass
A licence file is present (LICENSE).
Maintainer activity
Pass
The latest commit is within the last 365 days.
Note
Hygiene check of commit 01e5039eba5a. requests shell access. No manifest field names shell or command execution. can delete files. runs a script at install time. can reach a host that is not written as a fixed address. reads a credential or environment file. contains an encoded blob in a file that should be readable.
Date and source
Date checked:
github.com
Commit graded: 01e5039eba5a76b5078d946edf12d73a307a300e
This link goes to the original host. PlugVet does not host or check what you download from there, and installing it is your own decision and risk.