

MCP, MCP server
TaskChampion MCP
A Model Context Protocol server for Taskwarrior 3.x, TaskChampion, and Timewarrior.
Compatibility: Not stated.
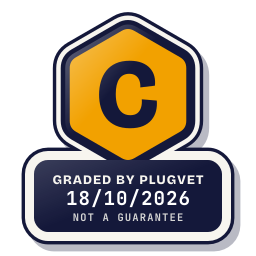
Grade C
One Medium finding. Read the findings before installing.
Not a guarantee. A hygiene check of the source at the commit shown, not a security audit.
Rescanned at commit f5af7735c735, unchanged since the check below.
INSTALL_REMOTE_SCRIPT
Why this grade
- INSTALL_REMOTE_SCRIPT Medium
Fetches a script from the network and runs it (a pipe to a shell, or an install hook with a URL).
scripts/setup_remote.sh, line 112
[ "$DRY_RUN" = "true" ] || curl -LsSf https://astral.sh/uv/install.sh | sh
Any High, or two or more Medium findings, give D. One Medium gives C. Low findings or a security Note give B. Each code names a finding behind the letter.
If you think this grade is wrong, email [email protected] with the entry link and your evidence. We aim to acknowledge within two working days and decide within seven. If we confirm an error, we aim to correct it within 24 hours of confirming it. These are aims, not guarantees.
Grades are a hygiene check of the source at the commit shown, on the date checked, not a security audit or a guarantee. The free directory grades are automated. Before release, a PlugVet engineer reviews every paid report and any grade we hold back, including all F grades, against the source code and the evidence we quote.
What was checked
Plain notes from the hygiene checks.
Permissions
Note
requests shell access. The manifest names this permission.
PERMISSION_SHELL_DECLARED
src/taskchampion_mcp/cli.py, line 71
proc = subprocess.run(
docs/adrs/ADRs.md, line 418
1. **Subprocess argument lists** - all CLI calls use `subprocess.run()` with argument lists, never `shell=True`. This is the primary command injection defense.
docs/adrs/ADRs.md, line 550
A second pressure is the subprocess boundary: most bugs in a CLI-wrapping MCP server live in argument construction and output parsing, neither of which is exercised by unit tests t
Show more
docs/adrs/ADRs.md, line 556
1. **Unit tests** (`tests/`, fast, run on every commit). Mock `subprocess.run` and the filesystem where helpful. Cover sanitizer rules, schema validation, rate limiter, config load
docs/llm_context/assumptions_and_ideas.md, line 36
### ASM-004: `subprocess.run()` with list arguments prevents shell injection
docs/manuals/security_model.md, line 13
- CLI calls use `subprocess.run()` with **argument lists** - never
Install and update
Serious
install fetches a script from the network. The docs document an installer that pipes a download into a shell.
INSTALL_REMOTE_SCRIPT INSTALL_DOCUMENTED_INSTALLER
scripts/setup_remote.sh, line 112
[ "$DRY_RUN" = "true" ] || curl -LsSf https://astral.sh/uv/install.sh | sh
scripts/setup_remote.sh, line 114
echo " Install: curl -LsSf https://astral.sh/uv/install.sh | sh"
Network
Concern
can reach a host that is not written as a fixed address.
NETWORK_NO_FIXED_HOST
dev.sh, line 1192
echo " # or: curl -L https://github.com/modelcontextprotocol/registry/releases/..."
scripts/check_marketplace_visibility.py, line 59
with urllib.request.urlopen(req, timeout=TIMEOUT) as resp:
scripts/publish_smithery.sh, line 172
http_code="$(curl -sS -o /tmp/smithery-server-get.json -w '%{http_code}' \
Show more
scripts/publish_smithery.sh, line 178
http_code="$(curl -sS -o /tmp/smithery-server-create.json -w '%{http_code}' \
scripts/publish_smithery.sh, line 195
http_code="$(curl -sS -o /tmp/smithery-server-update.json -w '%{http_code}' \
scripts/publish_smithery.sh, line 214
http_code="$(curl -sS -o /tmp/smithery-release.json -w '%{http_code}' \
scripts/publish_smithery.sh, line 247
http_code="$(curl -sS -o /tmp/smithery-deploy.json -w '%{http_code}' \
Secrets
Pass
No read of a credential file or secret environment variable found.
Agent instructions
Pass
No instruction to ignore earlier instructions or to hide a step.
Obfuscation
Pass
No encoded or minified payload found.
Licence
Pass
A licence file is present (LICENSE).
Maintainer activity
Pass
The latest commit is within the last 365 days.
Note
Hygiene check of commit f5af7735c735. requests shell access. The manifest names this permission. install fetches a script from the network. The docs document an installer that pipes a download into a shell. can reach a host that is not written as a fixed address.
Date and source
Date checked:
github.com
Commit graded: f5af7735c735381e1cfd6179787e652d31fc8603
This link goes to the original host. PlugVet does not host or check what you download from there, and installing it is your own decision and risk.